
Blockchain-based document verification doesn't put your diploma on a public ledger for the world to see. Instead, it typically records a cryptographic fingerprint of the document, the issuer's identity, and a timestamp. That small footprint is what gets compared against the file someone hands you later.
This article covers how these systems work, where they genuinely help, their privacy architecture, and how they fit into higher-education admissions. One caveat up front: blockchain strengthens integrity checks, but it doesn't replace issuer governance, identity verification, or sound fraud review.
Key Takeaways
- Hashing detects whether a file changed; signatures confirm who issued it.
- Privacy-conscious systems keep student records and PII off-chain, not on-chain.
- Verification speed depends on network design, integrations, and key management, not the blockchain label alone.
- Blockchain adds the most value when multiple independent parties need a shared, tamper-evident record.
Why Traditional Document Verification Falls Short
Most institutions still verify documents the way they did two decades ago: an admissions officer emails the issuing registrar, waits for a reply, then cross-checks a PDF by eye against a sample template. It's slow, inconsistent, and doesn't scale.
The timing problem is real and measurable. NACES-affiliated evaluation providers often run 12 to 16-week decision cycles, roughly double what most institutional targets allow, based on TruEnroll's internal benchmarking across partner admissions offices.
Delays compound when international transcripts travel by post or courier rather than digitally, a friction AACRAO has documented in its own member survey work. That data reflects a small, nonscientific sample rather than a national average.
Why this matters for enrollment:
- 68% of applicants accept the first offer they receive (TruEnroll internal data), often within 72 hours versus a two-week institutional standard
- Universities lose an estimated 20 qualified candidates per month to faster competitors, or roughly $500k in annual tuition revenue at risk
- Manual review alone catches less than 15% of sophisticated digital alterations, per TruEnroll fraud-detection research

Fraud Isn't Always a Doctored PDF
Sometimes the document is unaltered—but the issuer isn't legitimate. In 2023, the Justice Department documented a scheme involving more than 7,600 fraudulent nursing diplomas sold from accredited Florida nursing schools, with a school owner among those convicted. The documents looked legitimate because, in a sense, they came from a real institution's compromised issuance process.
That distinction matters. Verifying a file's integrity is not the same as confirming its academic meaning, transfer-credit value, or compliance with institutional policy. A matching hash tells you the document wasn't edited after issuance. It says nothing about whether the issuer itself was honest.
How a Blockchain-Based Document Verification System Works
Three roles make up the standard model:
- Issuer: the university, licensing board, or employer that creates and signs the original record.
- Holder: the student, applicant, or employee who receives and presents the document.
- Verifier: the admissions office, registrar, employer, or regulator checking it.
Hashing: The Document's Fingerprint
When a university finalizes a transcript, the file (or specific fields within it) gets run through a cryptographic hash function. NIST's SHA-256 standard produces a 256-bit digest: a fixed-length string unique to that exact input.
Change one character and everything shifts. Swap a grade from "B+" to "A-" on an otherwise identical transcript, and the resulting hash becomes a completely different string. There's no partial match. It's either the same document or it isn't.
What Gets Recorded on the Blockchain
This is the part people often get wrong: the full PDF doesn't need to go on-chain. What typically gets recorded is minimal:
- The document hash
- An issuer identifier or public key
- A timestamp
- A credential reference and status (valid, revoked, expired)
The original file and any personally identifiable information stay in controlled, off-chain storage. Whether the network is permissioned (controlled membership) or public (open participation) changes who can see that metadata and who bears the operating cost. Either way, the sensitive document content stays off the ledger.

The Verification Step
When someone needs to confirm a document, the process generally runs like this:
- The holder uploads the file, scans a QR code, or shares a verification link.
- The system recalculates the hash from the presented document.
- That hash gets compared against the on-chain record and the issuer's signature.
- A result returns: verified, altered, revoked, expired, unknown issuer, or unable to verify.
A matching result confirms the file hasn't changed since issuance and that it ties back to a specific issuer key. It does not confirm that the data entered at issuance was accurate, or that the issuing organization is legitimate and accredited.
Benefits and Use Cases for Blockchain Document Verification
Done well, this approach produces four concrete operational gains:
- Fewer repeat verification requests: verifiers check a hash instead of calling the registrar every time.
- Consistent results: automated signature checks replace subjective visual review.
- A durable audit trail: timestamps show when a record or its status last changed.
- Scalability: the process holds up during high-volume admissions cycles without adding headcount.
MIT's early implementation is a useful reference point. Its 2017 digital diploma pilot offered a cohort of 111 graduates a credential anchored by a one-way hash and timestamped transaction; diploma contents stayed off-chain.
Graduates could share a file or link, and employers checked the digital record instead of relying on appearance alone. That pilot demonstrated portability. It did not publish quantified fraud-reduction figures, so treat similar vendor claims the same way: ask for the data.
Beyond higher education, the same architecture applies to:
- Workforce onboarding credentials and professional licenses
- Healthcare certifications (nursing boards, medical licensure)
- Government-issued licenses and permits
- Supply-chain and financial compliance certificates
Payoffs differ by role:
- Universities: stronger provenance and fewer manual verification cycles
- Students: a portable record reusable across applications without requesting new copies each time
- Employers and admissions teams: faster checks of issuer-backed evidence before a decision
TruEnroll's document verification engine runs a parallel forensics scan, checking more than 70 fraud indicators (watermarks, metadata, and signature patterns) on every submitted transcript in roughly three seconds, independent of whether a blockchain record exists.
Designing a Secure and Practical Verification System
Privacy, Keys, and Lifecycle Controls
The safest architectures follow a simple rule: record the minimum, store the rest off-chain.
- Keep original documents and PII in encrypted, access-controlled storage, not on the ledger.
- Record only the hash, issuer ID, and status needed for a verifier to do their job.
- Apply FERPA-aware consent and disclosure rules; electronic consent must authenticate its source, per Department of Education guidance.
- Treat signing keys like crown jewels: NIST's key management guidance recommends defined cryptoperiods, controlled rotation, and compromise-notification procedures, and generally discourages long-term backup of private signature keys.
Revocation deserves its own attention. A blockchain record is immutable, but a credential can still become invalid. A separate status registry lets verifiers see "unchanged since issuance" and "currently valid" as two different questions. Corrections should create a new, traceable issuance, not silently overwrite the original hash.
Permissioned vs. Public Networks: When to Skip Blockchain Entirely
| Network Type | Governance | Best Fit |
|---|---|---|
| Permissioned (e.g., Hyperledger Fabric) | Known, vetted participants | Controlled institutional consortiums |
| Public | Open participation, broader independent checking | Cross-border or multi-party trust needs |
Not every verification problem needs a chain at all. If a single trusted registry can serve as the source of truth, a digitally signed PDF or a secure institutional database often does the job with less overhead. Reach for blockchain when independent parties need a shared, tamper-evident record and no single organization should control the definitive version. Skip it when a simpler signed-record system already meets the requirement. Do not add blockchain as a label.
Implementing Blockchain Verification in Higher-Education Workflows
From Credential Creation to Admissions Decision
The workflow typically runs in sequence:
- An issuer signs the record
- The applicant holds and presents it
- Admissions or registrar staff verify issuer identity, integrity, and status
- The result feeds into the review and audit system
For this to work operationally, the verification layer needs secure API connections into document intake portals, CRM, SIS, and identity systems. It also needs a defined path for failed, expired, or unrecognized credentials to route to a human reviewer rather than stalling the application.

Pairing Verification with Credential Evaluation
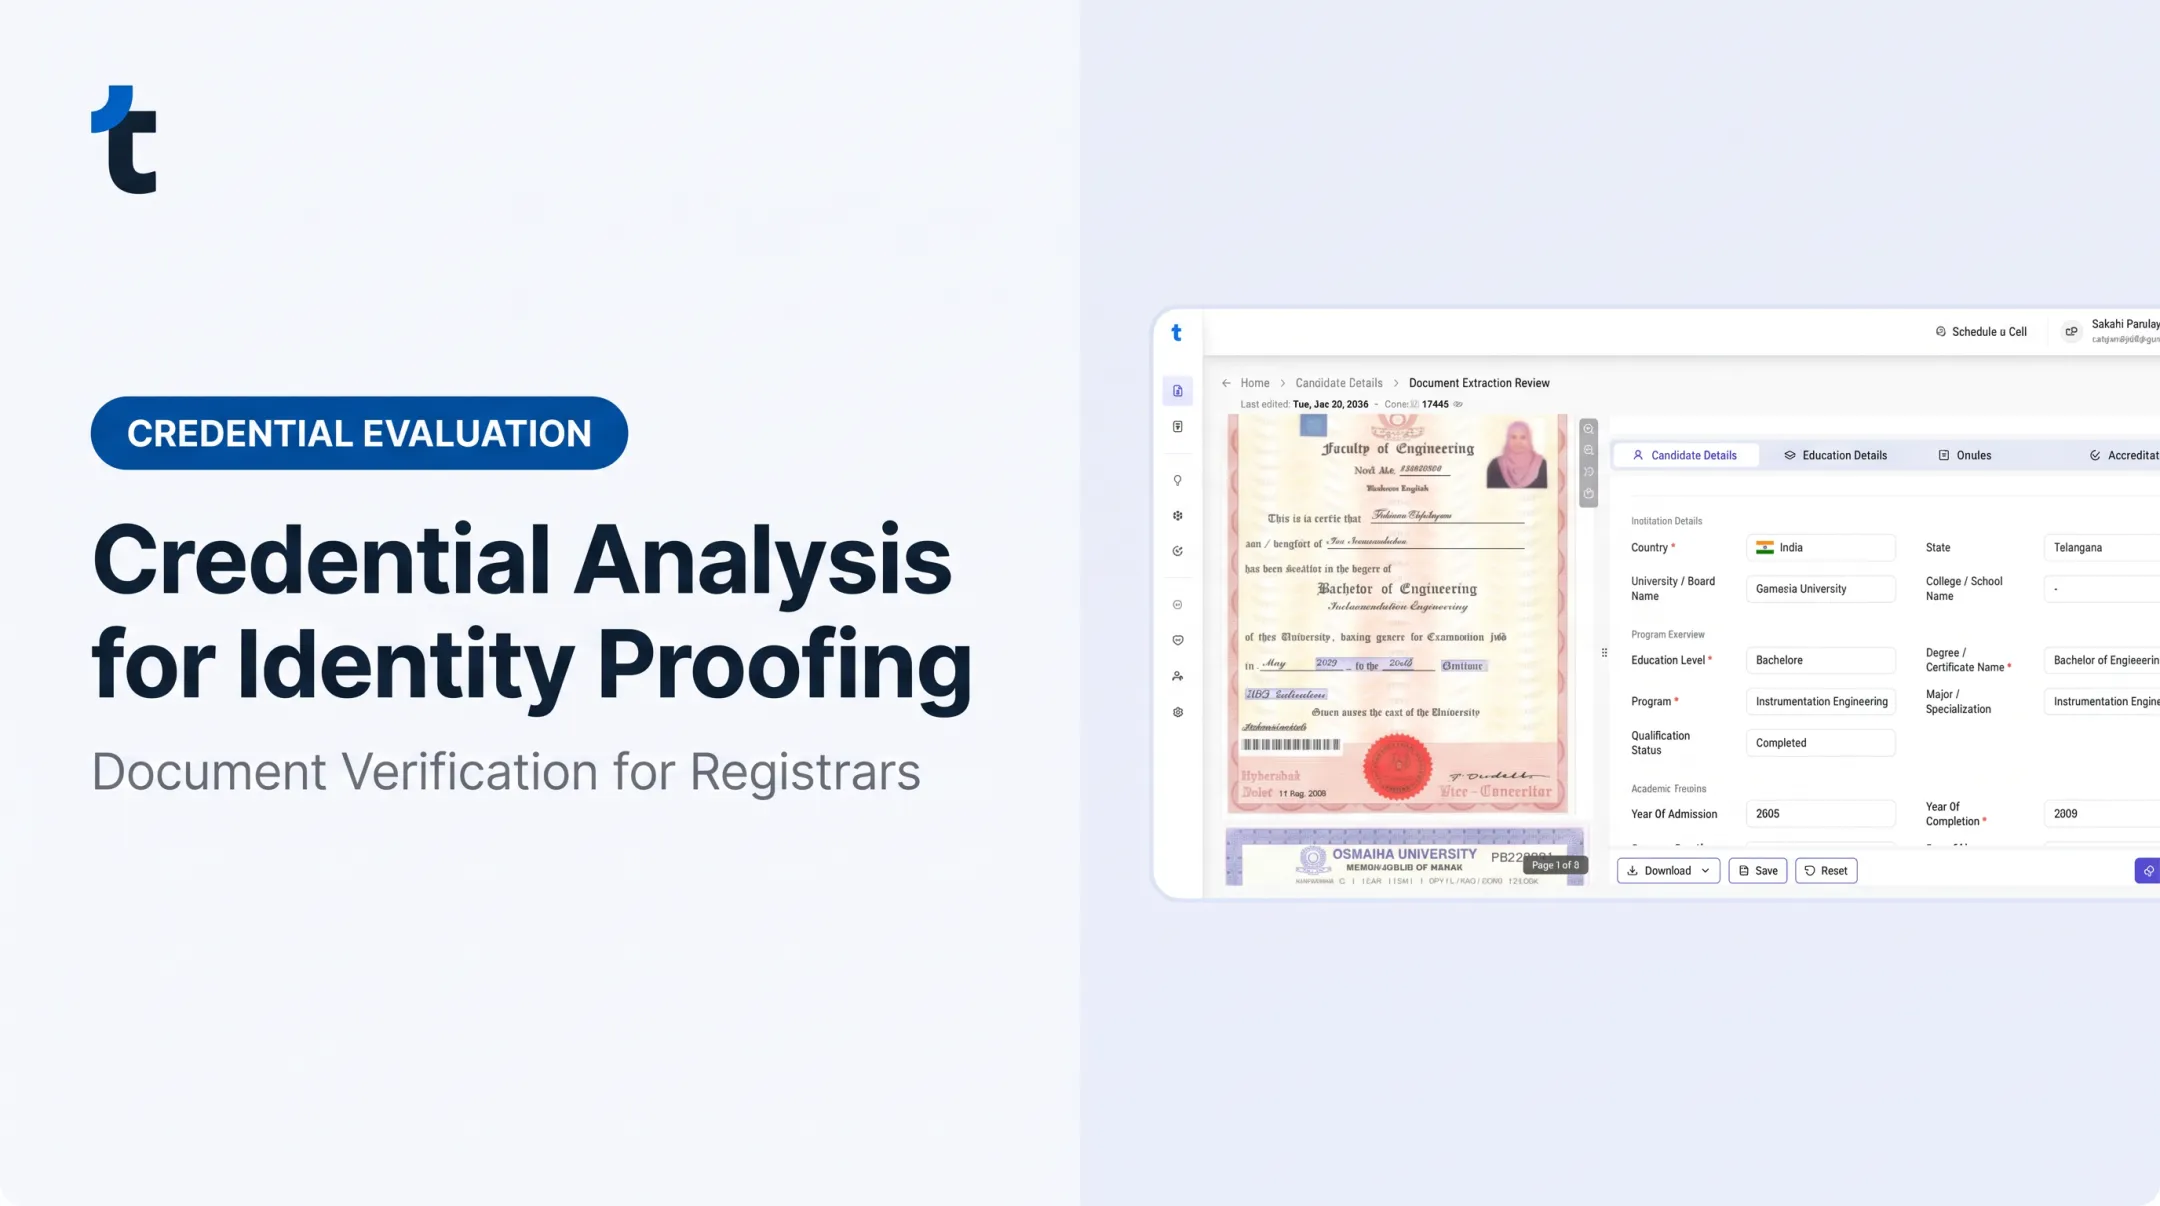
Here's the gap blockchain alone doesn't close: confirming a document is unaltered tells you nothing about what the coursework actually means for admission. That's a separate evaluation problem, and one TruEnroll was built to solve.
An institution could pair a blockchain verification layer with TruEnroll's AI-native transcript processing:
- Field-level provenance
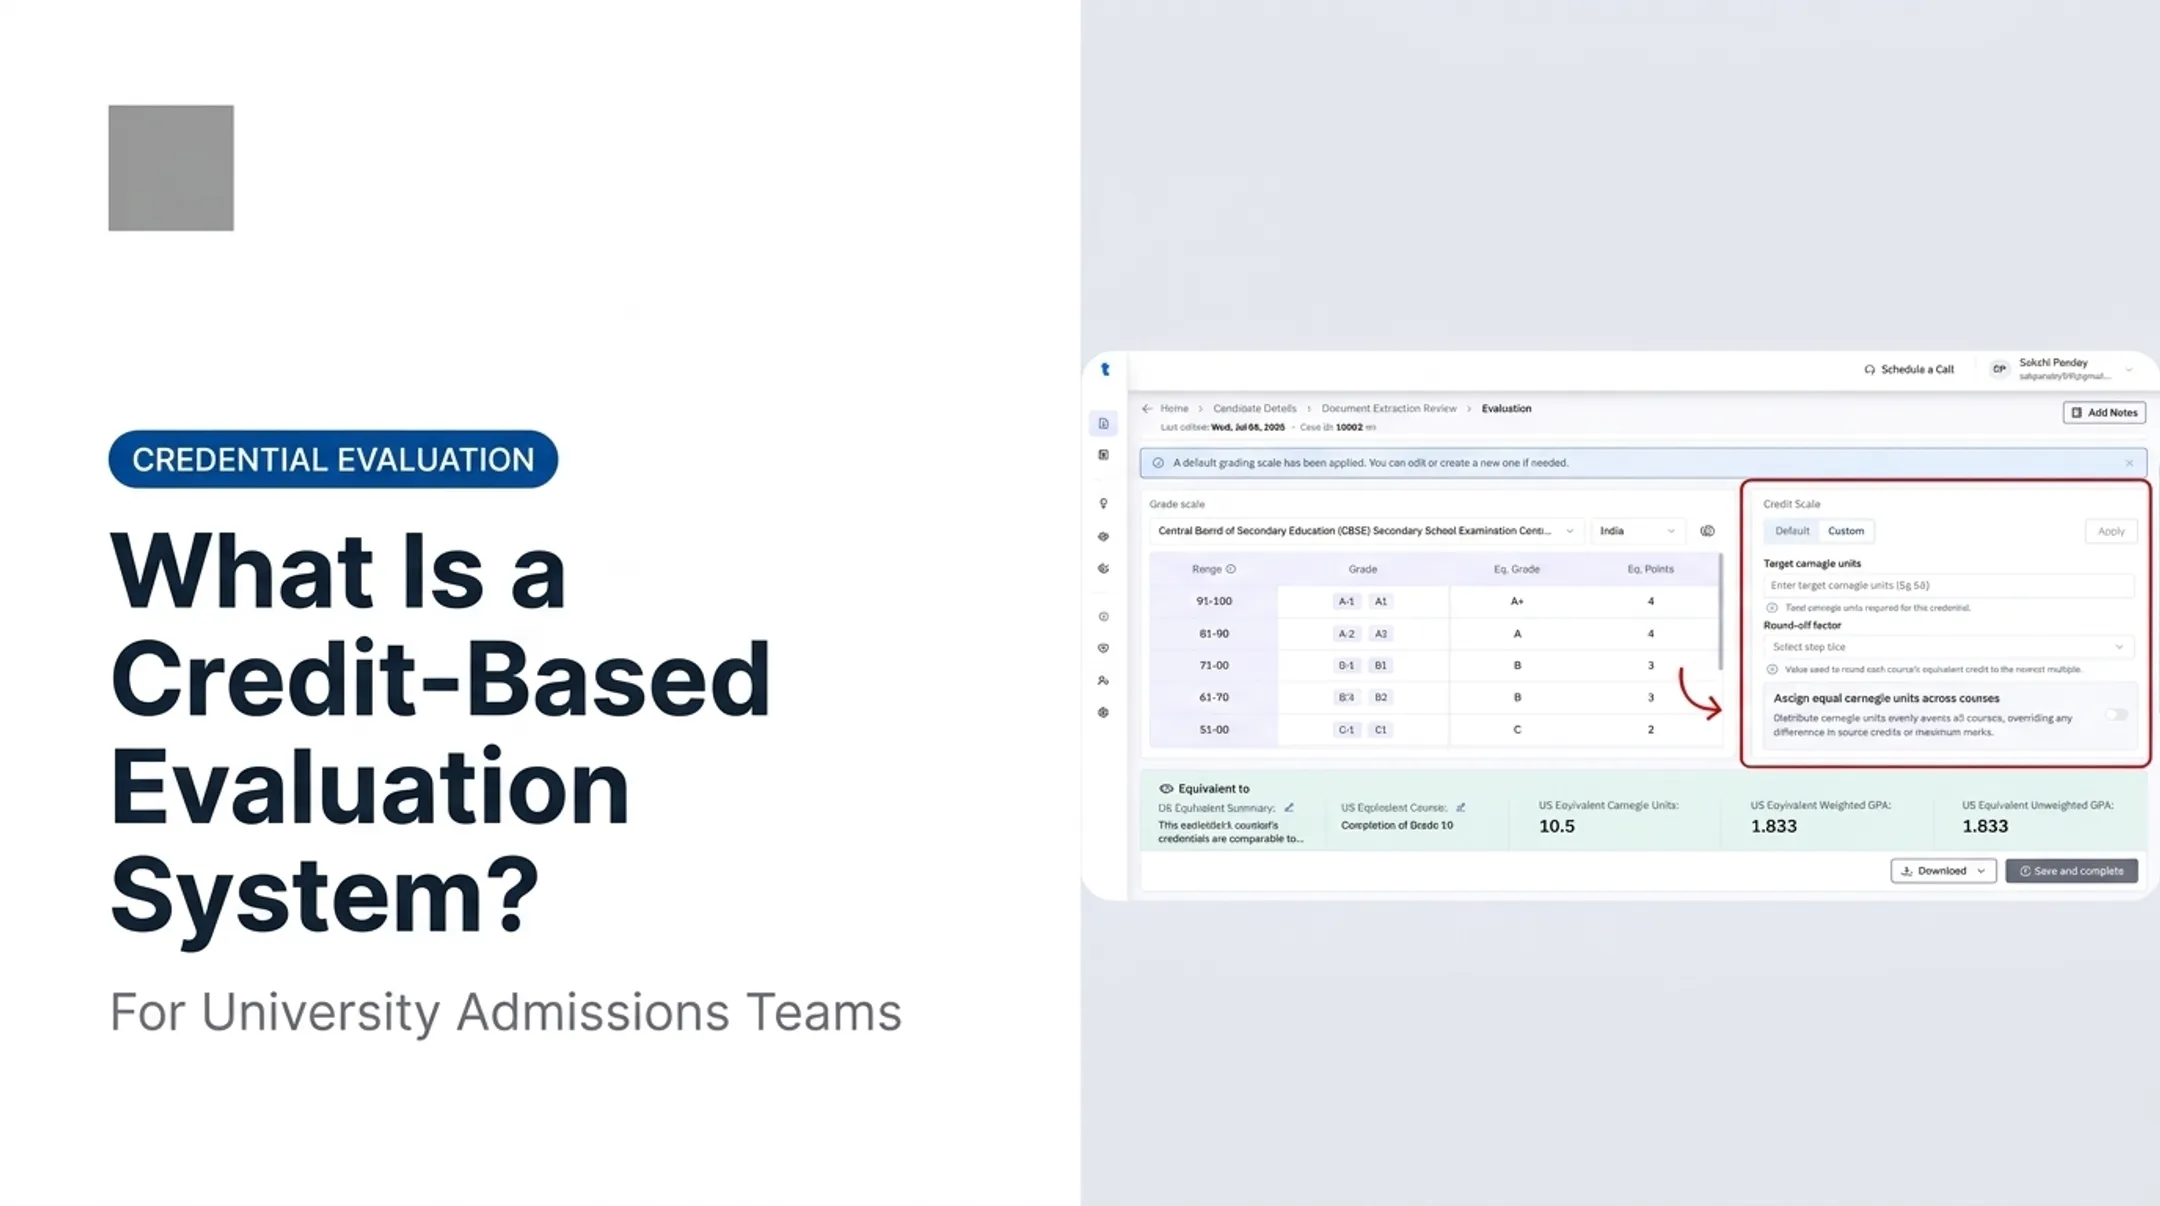
- Policy-aware credit evaluation
- Fraud detection that flags inconsistent or unrecognized institutions
- Direct sync into Slate, Banner, or Salesforce without CSV exports
TruEnroll is designed for high-volume transcript and admissions workflows and holds SOC 2 Type II, ISO 27001, and ISO 27701 certifications. The two layers address different parts of the pipeline (provenance versus evaluation) and work better integrated than treated as substitutes.
Readiness Checklist
Before piloting, map out:
- The specific trust problem you're solving (and whether it truly needs multiple parties)
- Document types and issuer network you'll onboard first
- Your off-chain privacy model and data residency requirements
- Integration points with existing SIS/CRM systems
- Revocation approach and key custody plan
- A fallback process for exceptions, plus how you'll measure success and total operating cost
Pilot one credential type before expanding across domestic and international records.
Building Trust Without Creating New Privacy Risks
Blockchain-based document verification adds a tamper-evident layer for checking whether a record matches what was issued. It needs several controls that do not run on autopilot just because a ledger is involved:
- Cryptographic hashing
- Issuer authentication
- Secure off-chain storage
- Revocation controls
- Interoperable formats
- Human review for exceptions
For admissions teams, the strongest setup pairs verifiable document provenance with accurate transcript evaluation, fraud detection, and audit-ready synchronization into the systems you already use. Start with the trust problem and privacy requirements, then choose blockchain or a simpler signed-record architecture based on what the evidence actually supports.
Frequently Asked Questions
Can blockchain be used for document verification?
Yes. It can record hashes, issuer evidence, timestamps, or status so a verifier can check whether a document matches the recorded version. It doesn't automatically prove the original content was accurate.
How long does it take for blockchain to verify your identity?
Document verification and identity verification aren't the same process. Timing depends on the network, transaction finality, congestion, and whether the system checks an existing record or creates a new one.
How does a blockchain-based document verification system work?
An issuer signs and hashes the document at issuance, then records the hash and issuer evidence. A verifier recalculates the hash from the presented file, compares it to the recorded version, and returns a verified, altered, revoked, or unresolved result.
Is blockchain document verification secure for personal data?
It can be, when designed with privacy in mind. That means keeping PII and full documents off-chain, recording minimal verification evidence, and layering in encryption, access controls, and key-management safeguards.
Does blockchain store the entire document?
Generally, no. Most responsible implementations store a hash or reference on-chain and keep the original document in secure, access-controlled off-chain storage.